If you’ve got people working from home, on the road, or across multiple sites, at some point they need to reach things that live back at the office — a shared drive, an internal system, a piece of finance software that was never built with remote access in mind. How you provide that access has changed a lot in the last few years, so here’s a plain-English look at where things stand.
The traditional answer: VPN
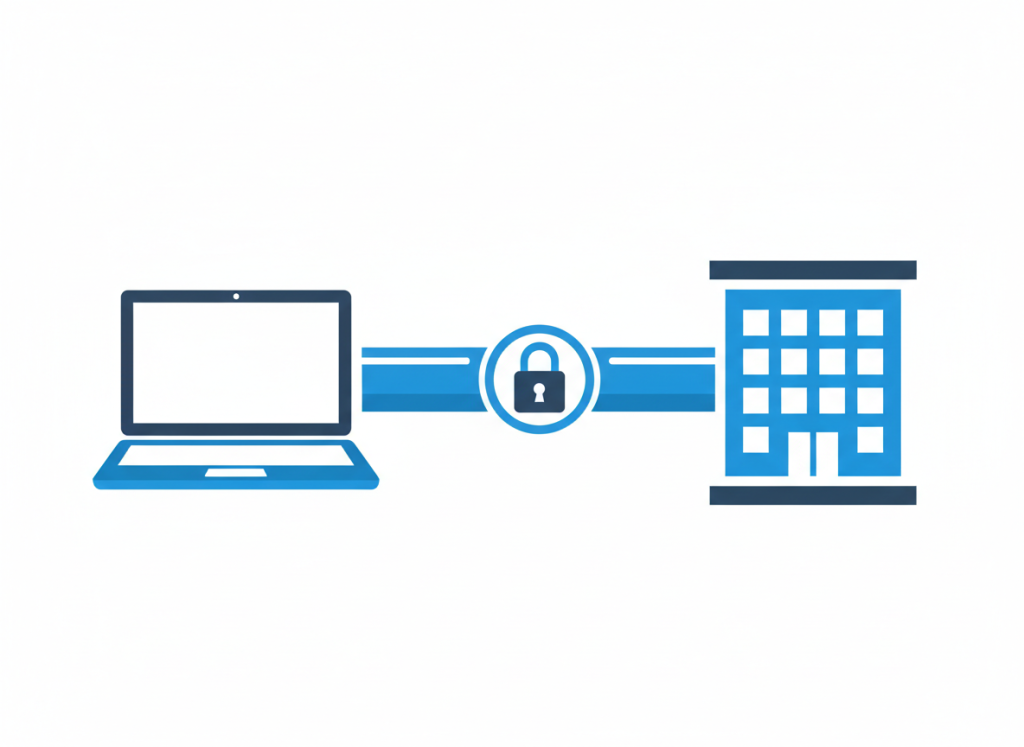
For a long time, a VPN (Virtual Private Network) was simply the tool for this job. The idea is straightforward: your laptop makes an encrypted connection back to the office network, and once connected, it behaves as if it were plugged in there — able to reach the same drives, printers and internal systems as if you were sat at your desk.
It solved a real problem, and for a lot of smaller setups it still works fine. But VPNs have some well-known drawbacks that become more obvious the more your business relies on remote and hybrid working:
- It’s all-or-nothing access. Once someone is connected, they’re typically on the whole network, not just the one system they need. If an account is compromised, whoever’s using it has a much wider reach than they should.
- Performance can suffer. All your traffic gets funnelled back through the office connection first, even if what you’re accessing (say, an app hosted online) has nothing to do with the office itself. That detour adds delay.
- It doesn’t scale well. Every additional user, every additional device, every additional cloud service adds more complexity to manage and more potential points of failure.
Why SASE is becoming the modern approach
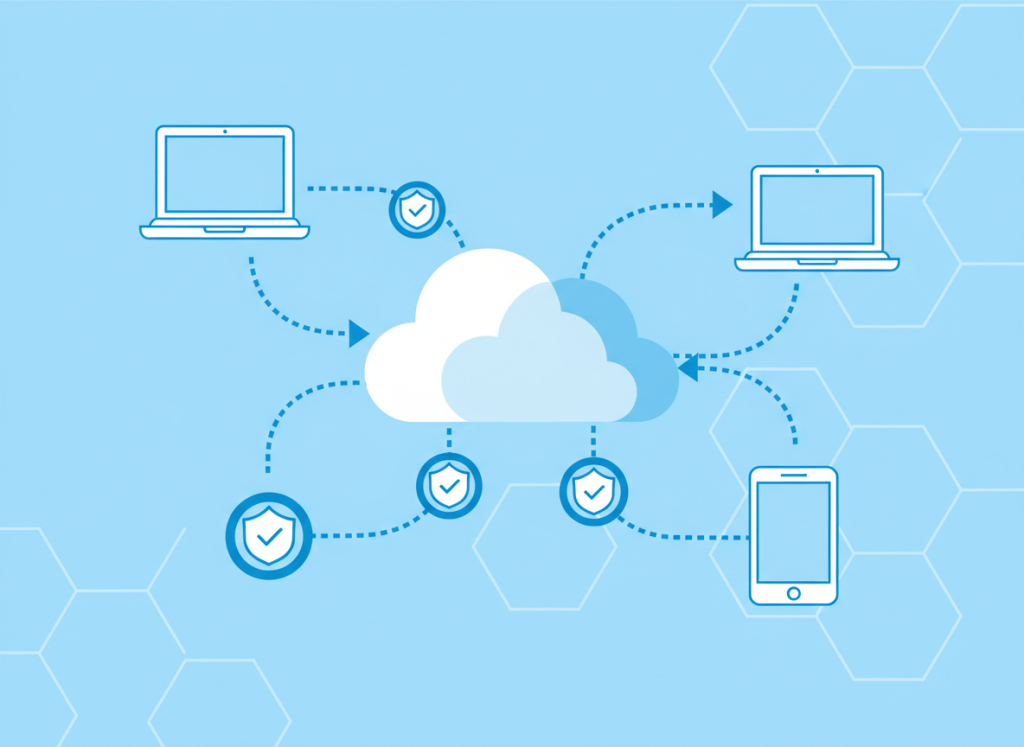
SASE (pronounced “sassy,” short for Secure Access Service Edge) is the approach that’s replacing VPN for a growing number of businesses. Rather than one encrypted tunnel back to a single office network, SASE builds security and access controls into the connection itself, wherever the user and the resource happen to be.
In practice, that gives you three things a traditional VPN doesn’t:
Better security. Instead of “connected = trusted,” SASE checks who’s asking, what device they’re using, and whether that request looks reasonable, every time — not just at login. It’s built around the idea that no one should be trusted automatically, even once they’re on the network. That matters a great deal if a password or a device is ever compromised, because the damage is contained rather than open-ended.
Better performance. Rather than a single connection point that everything routes through, SASE checks and connects users at a point of presence, close to wherever they actually are. This means less unnecessary detouring and a snappier experience, especially for cloud-based tools.
Much finer control over access. With a VPN, access tends to be broad by necessity. With SASE, you can set policy at a much more granular level — this person can reach this system, from this type of device, during these hours, and nothing more. That’s a far better fit for how businesses actually want to manage risk, and it makes life a lot easier when someone leaves the business or changes role.
What this means for you
If you’re currently relying on VPN and it’s working fine, that’s not an emergency. But if you’re finding it slow, if managing who has access to what is becoming a headache, or if you’re expanding your use of cloud-based systems, it’s worth having a conversation about whether a SASE approach would serve you better.
Get in touch and we’ll take a look at how your team works and what would suit you best.
